An executive’s public information can reveal more than any single post or record suggests. A professional biography, a property listing, an event announcement, and a family photograph may each be unremarkable on their own. Together, they can reveal locations, relationships, or routines that deserve a closer look.
That does not make every digital trace a threat. The important distinction is between information being available and evidence that a person or group may use it in a way that affects the principal’s safety or privacy.
Red5 Security, a protective intelligence and security advisory company, helps clients assess how digital exposure and changing threat information intersect with executive protection and personal risk.
Availability Is Not the Same as Intent
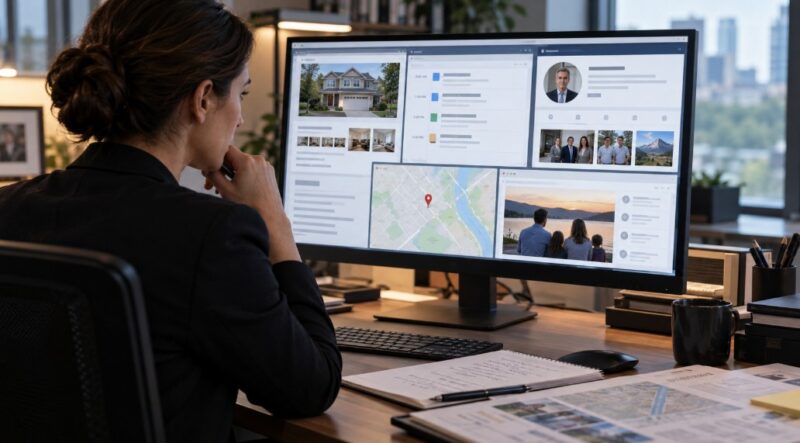
Public records, social-media posts, corporate disclosures, and event details may make personal information discoverable. Accessibility alone does not establish hostile intent, and a privacy vulnerability is not proof of an impending physical attack.
Security teams may still have good reasons to review exposure before a threat appears. A residence can be unnecessarily easy to identify. A family’s travel arrangements may be shared more widely than necessary. A vendor may retain access to sensitive information after an engagement ends.
Those are practical issues worth addressing on their own terms, without presenting every disclosure as evidence of an adversary.
Patterns Matter More Than Isolated Mentions
The assessment changes when public information intersects with concerning behavior. A general complaint about an executive differs from repeated unwanted contact. An anonymous post mentioning a city differs from a communication that accurately references a private address or a near-term schedule.
Analysts may consider the specificity, persistence, credibility, and progression of the activity. They also need to ask what remains unknown, including whether the source is authentic and whether the individual has demonstrated access or capability.
A threatening message can warrant attention even when attribution is impossible. Conversely, highly visible criticism may require no physical-security response when there is no credible indication of targeted risk.
Physical and Digital Security Inform Each Other
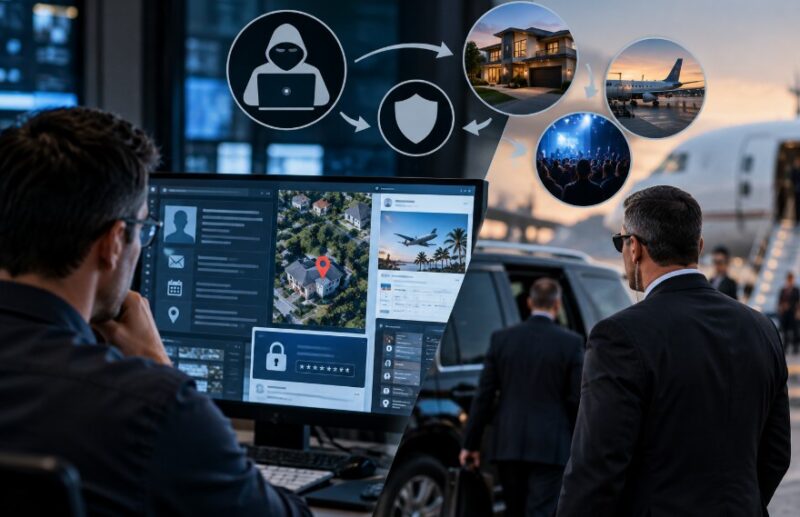
Digital information may influence decisions about a residence, a public event, or travel. Physical-security teams, in turn, may know details about access and routines that help analysts judge whether online information is meaningful.
If a private address is newly exposed during a period of credible threatening contact, a team might review residential arrangements or coordinate additional protective support. If a route is publicly announced before a contentious event, travel planners may consider alternatives. If an exposed credential suggests account compromise, cybersecurity specialists should handle the technical investigation and remediation.
Protective intelligence connects these concerns; it does not take over the work of every specialist involved.
Privacy Measures Should Be Proportionate
There are practical ways to reduce unnecessary exposure: limiting public itinerary details, reviewing information shared by vendors, checking the availability of personal records, and helping household members understand what should remain private.
Removal may not be possible for all information, especially when records are legally public or details have been widely copied. Privacy work should therefore focus on achievable reductions and on managing the consequences of information that cannot be withdrawn.
The aim is not to make a public-facing executive invisible. It is to reduce avoidable vulnerabilities while preserving the professional and personal activities that matter to the principal.
A Wider Range of Sources Can Provide Context
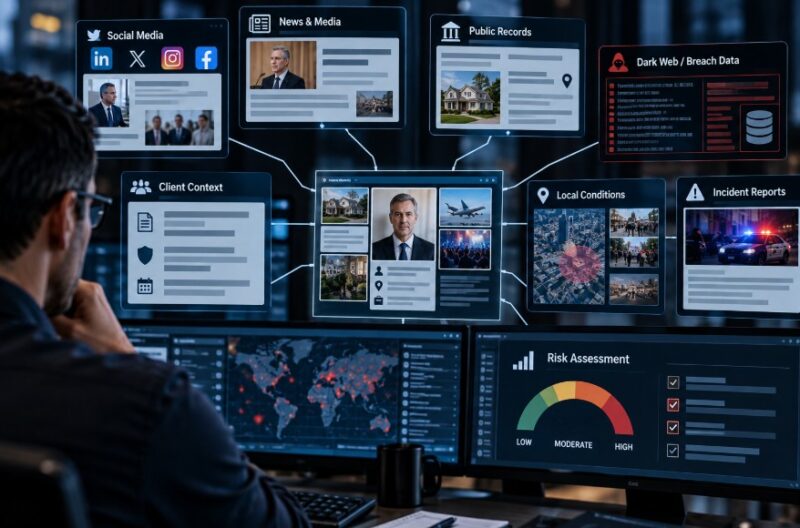
Open-source information is often relevant, but it is only one part of a protective intelligence assessment. Client-provided context, local conditions, credible reporting, and information about recent incidents may help explain why a particular exposure matters.
Compromised information circulating in illicit online environments can also be relevant in some cases. Such material requires careful validation and appropriate handling; its presence does not mean that the executive is about to be targeted.
The objective is to compare credible information from appropriate sources and determine whether it changes the risk assessment.
Turn Findings Into Decisions
A useful assessment should identify what is exposed, what is known about any concerning activity, what remains uncertain, and which measures could reduce risk. The result may be a privacy adjustment, further investigation, a change in protective coverage, or no immediate escalation.
That is a more defensible approach than assuming that every digital footprint predicts a real-world attack. It allows security teams to act when the evidence warrants action and avoid unnecessary disruption when it does not.
The Practical Role of Protective Intelligence
Digital exposure expands the questions executive security teams need to ask, but it does not erase physical perimeters or make physical surveillance irrelevant. Residences, access points, protective personnel, and emergency plans remain essential parts of the broader security picture.
Protective intelligence adds value by identifying meaningful connections between information and circumstances. The goal is not to collect every trace. It is to understand which exposures matter to this principal, in this situation, and what should happen next.